We wanted to use Baseten for inference. We had heard great things about their speed and reliability. So we went to check them out and... ended up with admin access to their core GitHub repositories.
Strix found a high-severity account takeover vulnerability in n8n, now tracked as CVE-2026-59208.
The flaw allowed identities from different trusted issuers to be mapped to the same local account.
Read the full technical breakdown below ↓
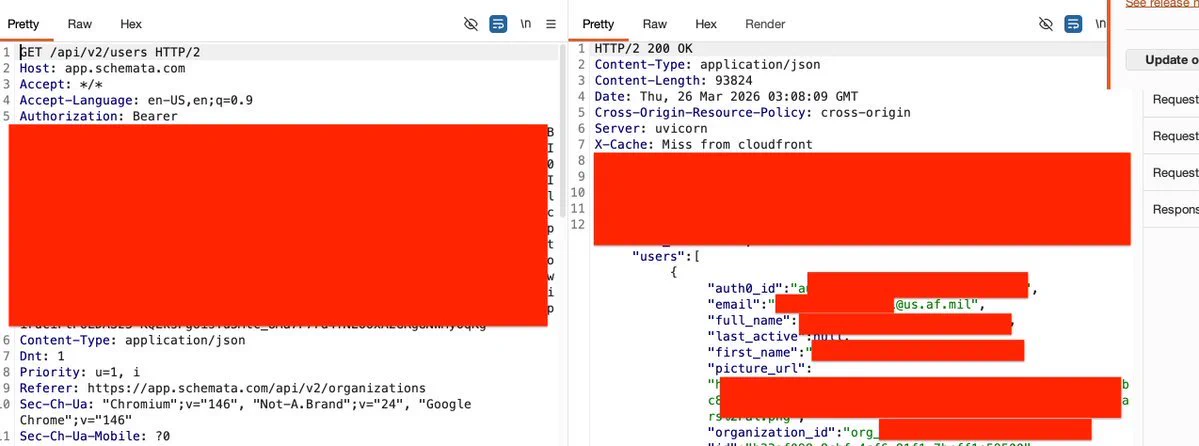
We found a zero-authorization vulnerability in an a16z-backed DoD startup that exposed the data of active U.S. military personnel.
We tried to report it. They ignored us for 150 days.
Here is how our open-source AI agent found the ultimate OPSEC nightmare 🧵👇